The process remembers.
XSSG discovers what's there, verifies what works, and moves through a defined security sequence. The critical steps don't live in a forgotten checklist or someone's head.
01
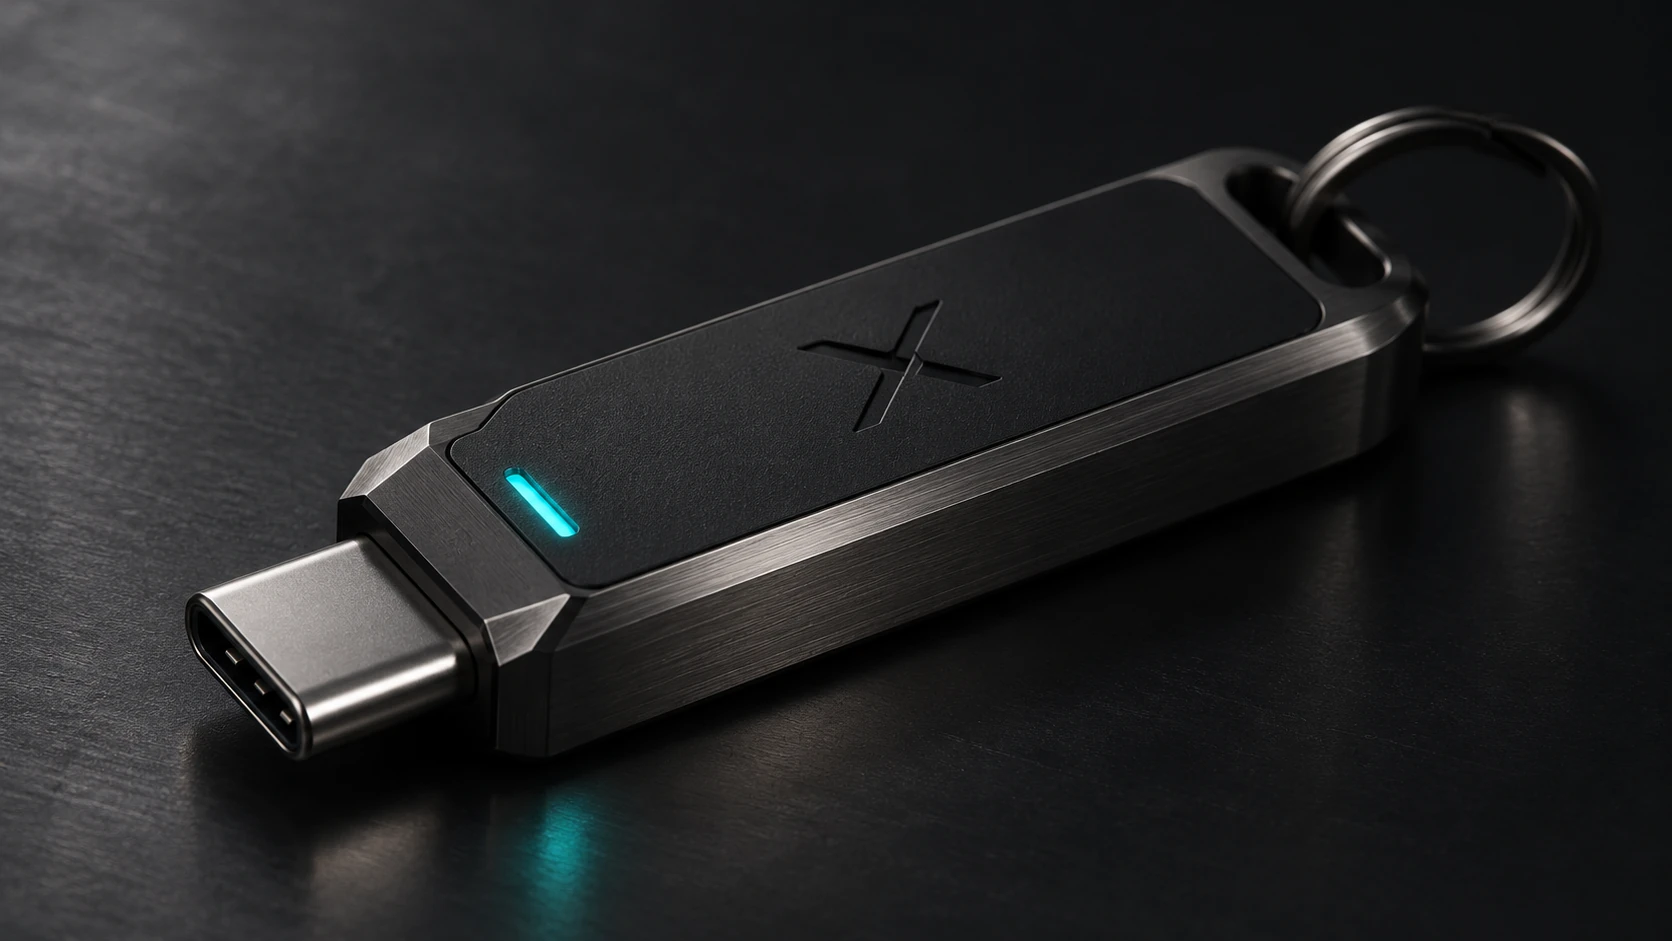
Give your SSH gateway the care it deserves. XSSG brings a guided, recovery-first security workflow to the hardware you already own. Verify key access. Seal an encrypted backup. Review every critical change. Finish with evidence.
XERXES Secure Shell Gateway · Reproducible. Modular. Recovery-first.
Hardware pictured is concept art. XSSG is software you can use with your own compatible USB drive.
Excellent tools invite confidence because every detail has a purpose. XSSG applies that principle to securing your own SSH service: powerful keys, protected recovery, visible decisions, and a guided path you can understand.
Careful operators have always understood this: the script isn’t the deployment. The verified procedure is. XSSG gives you that operating discipline on the machines you already own, and a recovery vault worth carrying.
From first connection through sealed vault to final evidence receipt.
Explore manual ↗NO MYSTERYHard questions about failures, passwords, FIDO2 and recovery.
Read Q&A ↗NO UNHACKABLE CLAIMSWhat passed in a live run—and what still needs controlled testing.
Review evidence ↗Manual SSH security gives skilled operators full control. XSSG adds a repeatable sequence, explicit checkpoints, and recovery verification—so the result is easier to inspect, maintain, and repeat.
XSSG discovers what's there, verifies what works, and moves through a defined security sequence. The critical steps don't live in a forgotten checklist or someone's head.
Healthy keys are reused. Verified vaults are reused. Unrelated systems are left alone. Re-running a security check should not become a junk-file factory.
Separate modules for discovery, keys, vaults, policy planning, guarded execution, and verification. Easier to reason about. Easier to test.
Back up the key. Unlock the vault. Restore a copy. Prove a fresh SSH login. Only then consider disabling password access and changing firewall rules.
Enterprise isn't a price tag.
It's discipline.
Expensive software doesn't make a deployment professional. Reproducible operations, guarded changes and verified outcomes do. XSSG brings that discipline to people who manage their own machines.
A vault stick with the restraint of a black-tie instrument: nothing decorative blocking its only job. Except here's the trick: you don't need to buy ours. Pick the drive you trust. XSSG turns it into your portable encrypted SSH recovery system.
A luxurious piece of hardware is nice. A verified recovery procedure is the actual luxury.
DESIGN CONCEPT · NOT A HARDWARE PRODUCTWatch the kind of security procedure XSSG conducts. This interactive walkthrough is an illustrative example—not a live connection or a real gateway audit.
“I don't want to hear that your system is unhackable. The first person who tries to sell you that fantasy is telling you more about their ego than their engineering.”
Here's the reality: we have assets worth protecting and threats that don't politely disappear. Destroying your asset defeats the point. Erasing every threat isn't a practical strategy. So we work with separation, controlled access, layered defenses and continuous measurement. That's why I respect the OSSTMM philosophy. Don't tell me what you installed. Show me what you tested. Show me what is still exposed. Then do it again tomorrow.
And to my fellow do-it-yourself engineers: ingenuity is admirable. Repeating a fragile ritual by memory isn't. Stop treating improvisation as sophistication. Put the knowledge into a repeatable system. That's what enterprises learned long ago. Now everybody can have it.
The current beta focuses on the repeatable SSH security workflow. We won't pretend the roadmap is already shipping.
Bring your own stick. Protect individual SSH keys in encrypted vaults. Verify a restored key by using it.
Read-only discovery, exact change preview, scoped UFW policy, protected SSH hardening and fresh key-only verification.
Hardware-backed SSH authentication is on the roadmap, with guided enrollment and the same recovery-first discipline.
More USB filesystems, remote pathways, failure-injection drills, and documented environment-specific verification.
No. The pictured drive is speculative XERXES concept artwork—not manufactured hardware, a promised bundle, or a product for sale. You choose your own compatible removable storage. XSSG stores encrypted vault files on it; the encrypted backup and wizard are separate.
The current beta is designed to identify and reuse a matching verified vault, rather than create duplicates. A changed key has a guarded replacement path. Older legacy backups are never silently erased.
No. Program installation does not import keys. Restoring is an explicit, selective action. Only the chosen key is installed when you request it.
Separate password checks verify separate actions: creating a vault, proving decryption, unlocking the SSH key, and authorizing remote Linux administration. XSSG does not persist or silently reuse these passwords.
Absolutely not. We reject that claim. XSSG aims to make well-defined security steps repeatable and verifiable, with explicit limitations and recovery mechanisms. It does not eliminate operational or threat-model risk.
No. XSSG currently configures and verifies SSH security on existing Linux gateways. It is not an SSH proxy, identity provider, or enterprise access broker.
Your keys. Your infrastructure. A guided path to a more defensible SSH configuration.
Beta 0.9.9-beta16 · Review release package before executing privileged software. Not production-certified.